01
The board pack is the risk program
Risks are listed once a year for the board. Between meetings, the real issues live in email and the ED’s head.
Audit prep shouldn't mean reconciling risk and compliance in two different systems
In the workspace
A program the board can trust between meetings
Risk
Programs and operations with real owners
Funders
Grant conditions on the same records
Board
Live residual risk, not an annual list
Non-Profits · Essentials
Charities and associations start with operational, funding, and reputation risk — then add grant, privacy, and governance obligations on the same workspace.


The work
You are accountable to a board, to funders, and to the people you serve — usually with a team that cannot staff a traditional GRC program.
01
Risks are listed once a year for the board. Between meetings, the real issues live in email and the ED’s head.
02
Funders require controls, reporting, and safeguarding. Those obligations are not mapped to the operational risks of the programs they fund.
03
Donor data, beneficiary data, and safeguarding are serious obligations run as side duties. There is no workspace that holds them next to operational risk.
04
A program failure or data event is public before the next board meeting. Residual risk was last discussed at the retreat.
In the workspace
A GRC program a lean team and a board can both use.
Program leads update the risks they own. The board sees residual movement without a special offsite document.
Conditions sit with the programs they fund. Reporting and evidence collection are workflows, not a scramble at year end.
Donor, member, and beneficiary obligations live next to the operational risks of the systems and programs involved.
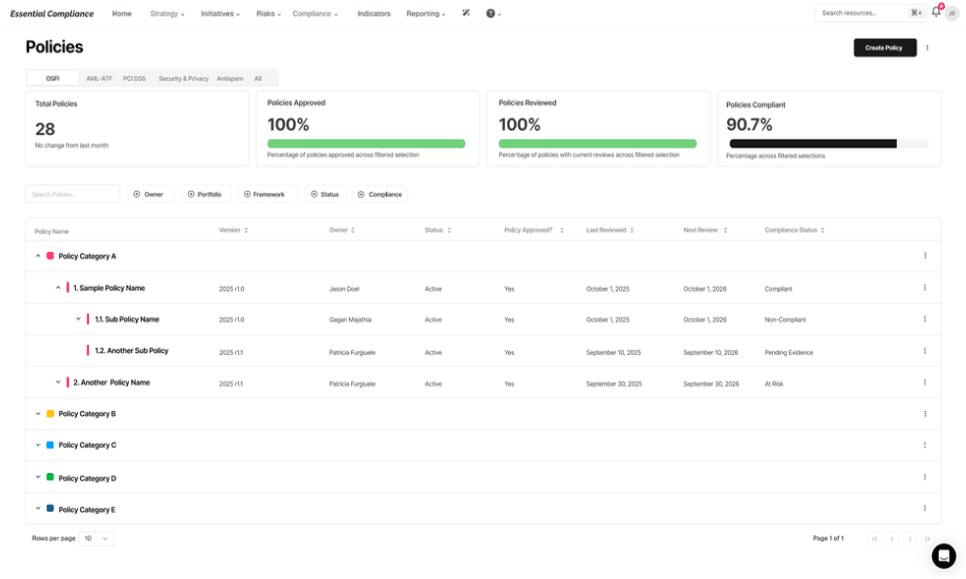
Actions, owners, and overdue items are visible. The board pack is a view of the workspace.
How Essentials shows up
Start with the risks the board already asks about. Add grant, privacy, and governance on the same records — at a scale a small team can run.


FAQ
Related industries
Explore how Essentials shows up in adjacent verticals.
Rapid Implementation
Risk Reduction
Organizations
Trusted by customers and rated highly across all categories
Trusted by 100+ organizations
Industry-leading security certifications and compliance standards
Annual third-party security audit
CertifiedInformation security management
CompliantEuropean data protection compliance
CompliantChoose the deployment model that best fits your security and compliance requirements
Every component of our platform is designed with security best practices, from the ground up. We implement defense-in-depth strategies to protect your most sensitive data.
Supporting 50+ compliance frameworks across 150+ countries


