A strong ERM or GRC software RFP does more than collect feature checkmarks. It explains the outcomes your organization needs, gives vendors realistic scenarios to solve, and creates a consistent record for comparing capability, delivery risk, and total cost.
The most useful RFPs are selective. They focus on the workflows and decisions that matter, require evidence for vendor claims, and test whether the platform will work for executives, risk owners, compliance teams, administrators, and occasional users.
Need a starting point instead of a blank document?
Explore our free enterprise risk management and GRC RFP template. All 112 requirement prompts, the scoring model, and vendor demo scenarios are readable online. A formatted PDF is also available.
What is a GRC RFP?
A governance, risk, and compliance request for proposal is a structured document used to tell software vendors what an organization needs and how proposals will be evaluated. It typically covers business objectives, functional requirements, technology and security, implementation, support, commercial terms, and selection rules.
An enterprise risk management RFP may focus on risk identification, assessment, appetite, indicators, controls, scenarios, treatment, and executive reporting. A broader GRC RFP can also include compliance, policy, audit, incident, third-party risk, assurance, and issue-management processes. The scope should follow the operating problem—not a vendor's module list.
The RFP serves two purposes. Externally, it gives vendors enough context to propose a credible solution. Internally, it forces stakeholders to agree on priorities and creates a defensible method for comparing options.
Before you write the RFP: align the buying team
Many weak RFPs begin with a spreadsheet of features. Start with the decision the organization is trying to make and the outcomes the platform must support.
Bring the right people together
A typical evaluation should involve:
- an executive sponsor who owns the business outcome;
- risk, compliance, audit, or assurance process owners;
- representative business users and risk owners;
- information security, privacy, architecture, and integration specialists;
- procurement, legal, finance, and records-management stakeholders; and
- the team responsible for implementation, administration, and adoption.
Agree the scope and success measures
Before drafting requirements, answer these questions:
- Which decisions or processes are currently slow, inconsistent, or poorly evidenced?
- Which entities, regions, frameworks, risk domains, and user groups are in scope?
- Which requirements are genuinely mandatory?
- What must be delivered in the first phase, and what can follow later?
- How will success be measured after implementation?
This prevents the RFP from becoming a collection of preferences with no connection to business value.
Seven sections every ERM or GRC software RFP needs
1. Organization context and target outcomes
Describe the current operating model, maturity, pain points, users, systems, regulatory environment, and intended outcomes. Vendors cannot design a credible approach if they do not understand what is changing or why.
2. Scope, volumes, and constraints
State the processes, business units, entities, regions, frameworks, records, integrations, historical data, environments, and user populations in scope. Include important dates, procurement rules, data-residency needs, and existing contractual dependencies.
3. Functional requirements
Organize requirements around actual workflows: risk assessment, appetite, KRIs, controls, obligations, evidence, issues, policies, audit, incidents, vendors, actions, and reporting. Ask vendors to describe how the capability works and what configuration or services it requires.
4. Platform, data, integration, and security
Cover identity, authorization, APIs, connectors, import and export, audit history, accessibility, architecture, hosting, encryption, privacy, resilience, incident response, and exit. Involve specialists early enough to influence selection, not only after a preferred vendor emerges.
5. Implementation, migration, adoption, and support
Require a proposed plan with customer and vendor responsibilities, migration assumptions, acceptance criteria, training, knowledge transfer, change management, support levels, and release practices. The buying decision includes a delivery model—not just a product.
6. Vendor and commercial information
Ask for relevant experience, comparable references, roadmap governance, financial stability, pricing assumptions, implementation costs, third-party dependencies, annual increases, renewal terms, and a realistic three- or five-year total cost.
7. Response and evaluation instructions
Define the response format, timetable, clarification process, demonstration rules, scoring scale, category weights, mandatory requirements, and evidence expectations. Vendors should know how they will be evaluated before they respond.
How to write GRC software requirements that reveal real differences
A yes-or-no requirement such as “Does the system support risk assessment?” tells you very little. Most vendors will answer yes, even when the workflows, configuration, evidence, or user experience differ substantially.
A stronger requirement asks the vendor to:
- describe how the capability works in the current product;
- identify whether it is standard, configurable, custom, third-party, or roadmap;
- explain implementation effort, dependencies, limitations, and separate costs;
- provide evidence or show the capability in a scripted demonstration; and
- state who administers and maintains it after launch.
| Weak requirement | More useful requirement |
|---|---|
| Supports risk appetite | Show appetite statements, measurable thresholds, breaches, approvals, escalation, and reporting at enterprise and business-unit levels. |
| Has integrations | Describe supported API and event patterns, authentication, limits, monitoring, versioning, error handling, and ownership for each required integration. |
| Provides dashboards | Build a board-ready view from supplied data, explain material movement, and drill from summary metrics to source records and evidence. |
Label each requirement as mandatory, important, or optional before proposals arrive. This makes the evaluation less vulnerable to impressive but low-priority features.
How to score ERM and GRC software vendors fairly
Agree the scoring model before opening responses. Use a documented scale—often 0 to 5—and define what each score means. Require comments and evidence for material scores, then moderate differences between evaluators.
| Category | What to assess | Example weight |
|---|---|---|
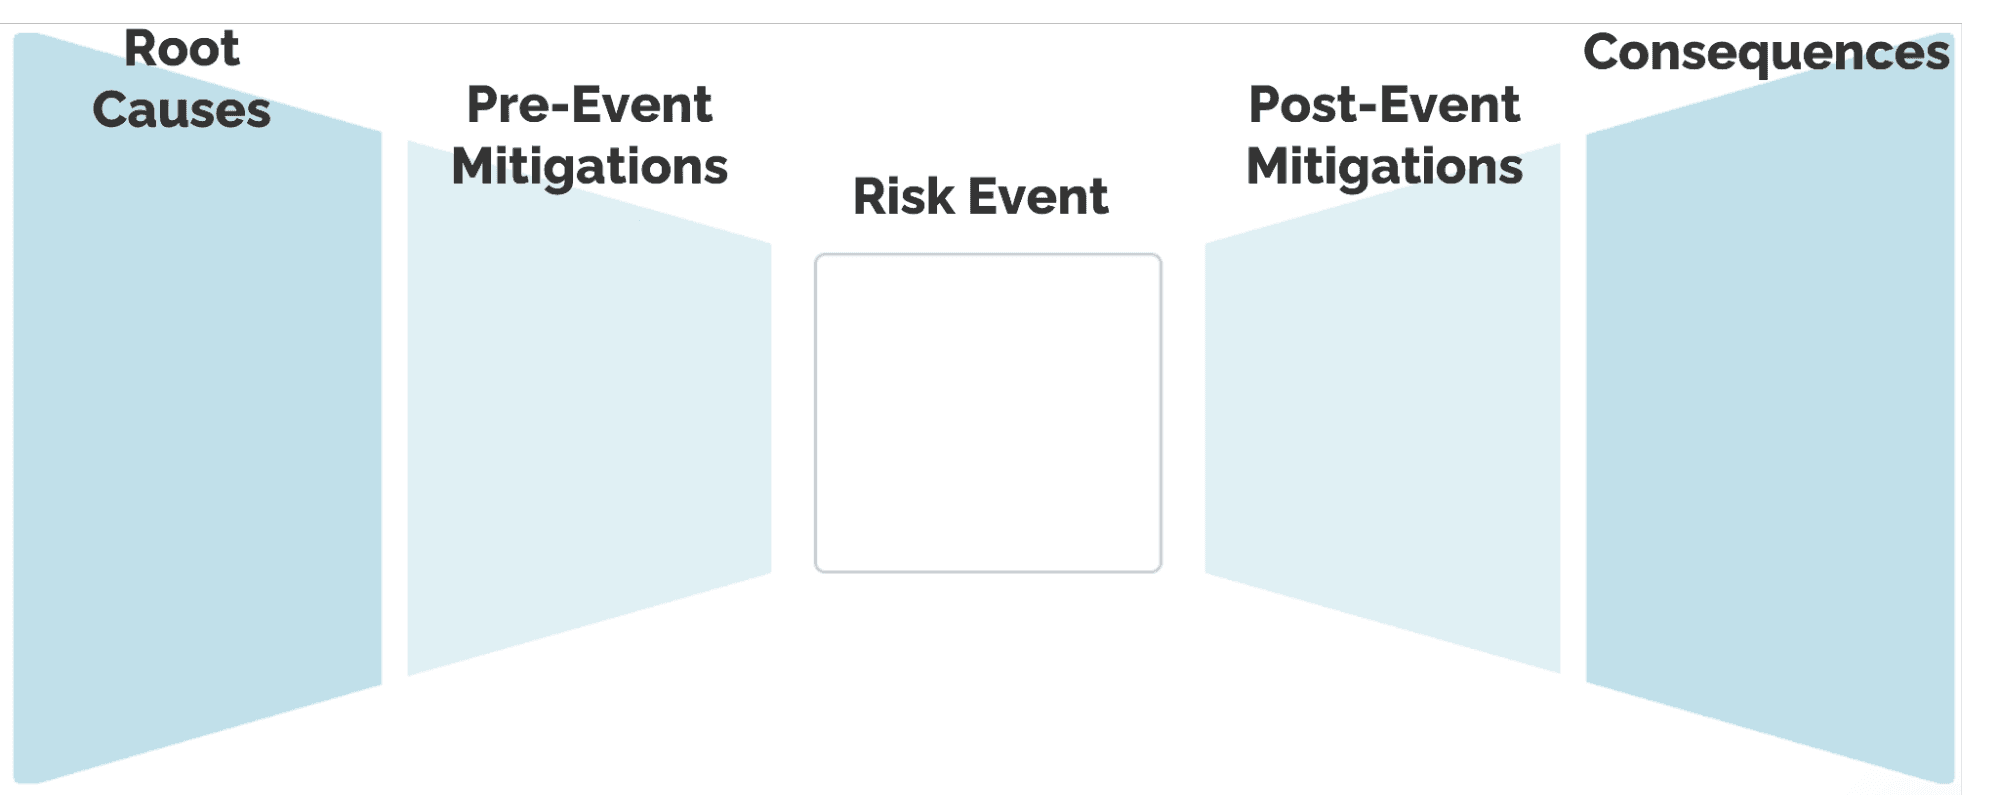
| Enterprise risk management | Risk taxonomy, registers, assessments, appetite, KRIs, controls, scenarios, bow-tie analysis, and board reporting. | 25% |
| Governance and compliance | Obligations, frameworks, policies, controls, evidence, attestations, testing, issues, and regulatory change. | 20% |
| Platform and user experience | Workflow configuration, search, dashboards, mobile access, notifications, accessibility, and administration. | 15% |
| Technology and security | Architecture, SSO, APIs, integrations, encryption, audit logs, resilience, privacy, and data portability. | 20% |
| Delivery and partnership | Implementation approach, migration, enablement, support model, roadmap, references, and total cost. | 20% |
Example weights are not universal. A regulated financial institution may place more weight on security, controls, and compliance. An organization replacing spreadsheets may place more weight on usability, implementation, and adoption.
Treat critical requirements separately. A high overall score should not compensate for failure on mandatory security, privacy, regulatory, accessibility, or data-exit needs. Evaluate total cost and implementation risk alongside the weighted capability score.
Turn GRC vendor demonstrations into evidence
Generic demos are optimized to show each product at its best. They are useful for orientation but poor for comparison. Give shortlisted vendors the same sample data and scripted scenarios, then score what they actually demonstrate.
A practical demonstration should test tasks such as:
- creating a strategic objective and linked risk, then mapping causes, controls, appetite, indicators, and treatment;
- assessing a new compliance obligation, reusing controls and evidence, and remediating a gap;
- escalating a failed control or overdue action and showing the resulting risk and compliance impact;
- changing an owner or organization structure while preserving history and access; and
- building an executive report from current data and drilling back to source evidence.
During every demo, ask four questions:
- Is this capability generally available in the proposed product?
- What configuration, integration, service, or additional license does it require?
- Who performs and maintains this work in production?
- What happens when the data is incomplete or the process fails?
Common GRC RFP mistakes—and how to avoid them
Starting with a giant feature list
A long checklist creates work without necessarily improving the decision. Begin with outcomes and critical use cases, then add only the requirements needed to test them.
Treating all requirements as equally important
When everything is mandatory, nothing is prioritized. Separate non-negotiable constraints from important capabilities and optional differentiators.
Accepting unsupported yes answers
Require explanations, product evidence, dependencies, limitations, and costs. Validate important claims in a demonstration or reference check.
Letting each vendor choose the demo
Vendor-led demos prevent comparison. Use common scenarios, data, time limits, and evaluators for every shortlisted product.
Evaluating software but not implementation
A capable platform can still fail through weak migration, governance, training, or adoption. Score the delivery approach and customer responsibilities.
Comparing subscription price instead of total cost
Include implementation, migration, integrations, additional environments, growth, internal effort, support, renewals, overages, and exit.
A practical GRC RFP timeline
The duration depends on scope, procurement rules, stakeholder availability, and the depth of diligence. More important than a universal schedule is a transparent sequence with realistic time for vendors to respond and evaluators to validate.
- 1Confirm scope, stakeholders, governance, and success criteria.
- 2Draft and prioritize requirements, scenarios, weights, and response instructions.
- 3Issue the RFP and manage all vendor questions through one documented channel.
- 4Score written proposals and send consistent clarification questions.
- 5Run scripted demonstrations with the same data, timing, and evaluators.
- 6Complete security, privacy, architecture, legal, commercial, and financial diligence.
- 7Check comparable references, moderate scores, and document the preferred option.
- 8Finalize scope, pricing, service levels, commitments, implementation, and exit terms.
Frequently asked questions
What is a GRC RFP?
A governance, risk, and compliance (GRC) request for proposal is a structured document used to explain an organization’s needs and compare software vendors consistently. It normally covers business outcomes, functional requirements, security and integration needs, implementation, support, pricing, and evaluation rules.
What should an enterprise risk management software RFP include?
An ERM software RFP should define the organization’s objectives and operating model, then test risk identification, assessment, appetite, controls, indicators, scenarios, reporting, workflows, integrations, security, implementation, support, and pricing. It should also include realistic use cases and a weighted scoring model.
How should GRC software vendors be scored?
Use a documented scale, such as 0 to 5, and multiply each score by an agreed category weight. Score mandatory requirements separately from differentiators, require evidence for vendor claims, and use the same scripted scenarios for every demonstration. Include total cost and implementation risk in the final decision.
How long should a GRC RFP be?
There is no universal length. A focused RFP that prioritizes outcomes and critical use cases is more useful than a large generic checklist. Provide enough detail for vendors to propose a credible solution, but avoid hundreds of low-value yes-or-no questions that do not distinguish between products.
Can this template be used for ERM-only procurement?
Yes. Keep the enterprise risk management, platform, technology, implementation, and commercial sections, then remove compliance or assurance requirements that are outside scope. Adjust the evaluation weights before issuing the RFP.
Start with the free ERM and GRC RFP template
Read and search 112 requirement prompts, compare example category weights, review a complete 0–5 scoring model, and use consistent vendor demo scenarios. The full resource is open in the browser; request the PDF only if you want a formatted copy to circulate.
The template is general procurement guidance. Tailor it with your organization's procurement, legal, security, privacy, accessibility, records-management, and financial specialists before issuing an RFP.