Back to all articles
NIS2ISO 27001Compliance|
Already ISO 27001 Certified? How to Use Your ISMS as the Foundation for NIS2 Compliance
Learn how organizations already using ISO 27001 can reuse existing policies, controls and evidence to address NIS2 requirements, identify gaps and manage both frameworks in one compliance program.

See How Leading Organizations Manage Risk
Join 100+ organizations using Tracker to streamline risk management, accelerate compliance, and turn governance into a strategic advantage.
Free demo · No commitment · See results in 30 days
Continue Reading
View all posts
GRCERM
How to Write an ERM or GRC Software RFP: A Practical Guide
Learn how to write an effective enterprise risk management or GRC software RFP, including requirements, evaluation criteria, vendor demo scenarios, scoring, and common mistakes.
 Tracker Networks Team|
SOC 2Vanta
Vanta and Sprinto Alternatives: Getting SOC 2 Right the First Time
What mid-market companies should know before choosing a compliance platform—including an honest look at Vanta, Sprinto, and what they do not tell you about what comes after the audit.
 Jason Doel|
risk managementbowtie
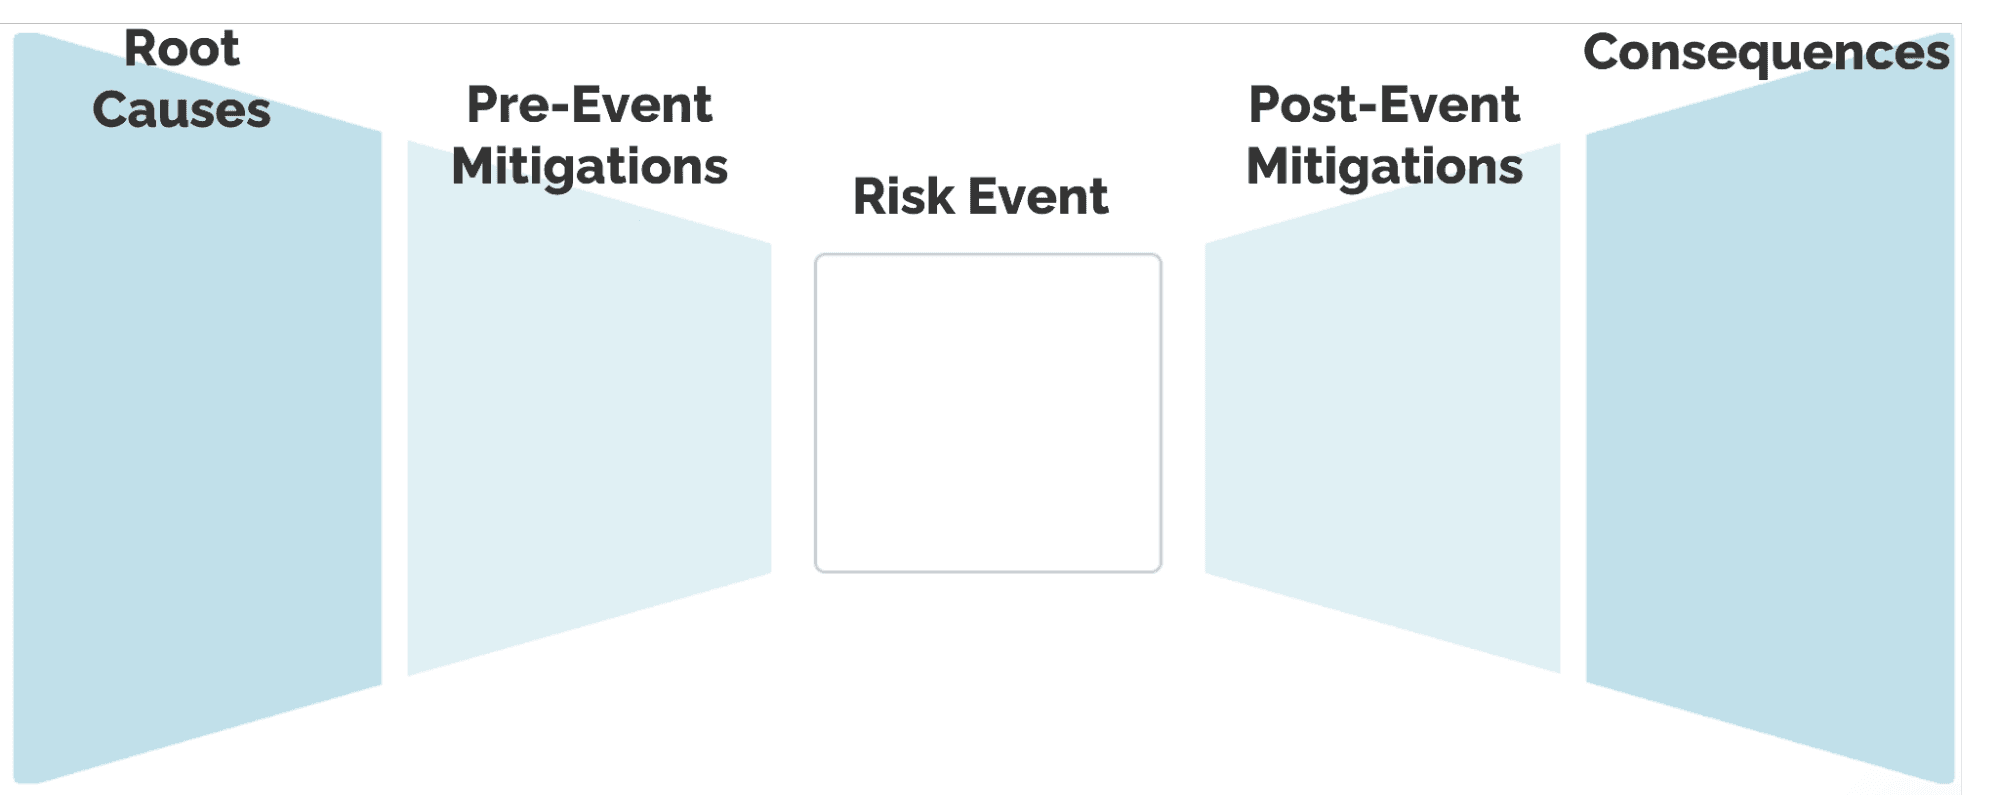
Bowtie Risk Assessment: A Practical Step-by-Step Guide
Learn the bowtie method of risk assessment with a practical, step-by-step guide. See when to use bowties, how to build them, and how to evaluate control effectiveness.
Jason Doel|Written by

Jason DoelCOO & CRO
Sep 3, 2026
15 min read


